
By Paulo Lilla and Carla Segala*
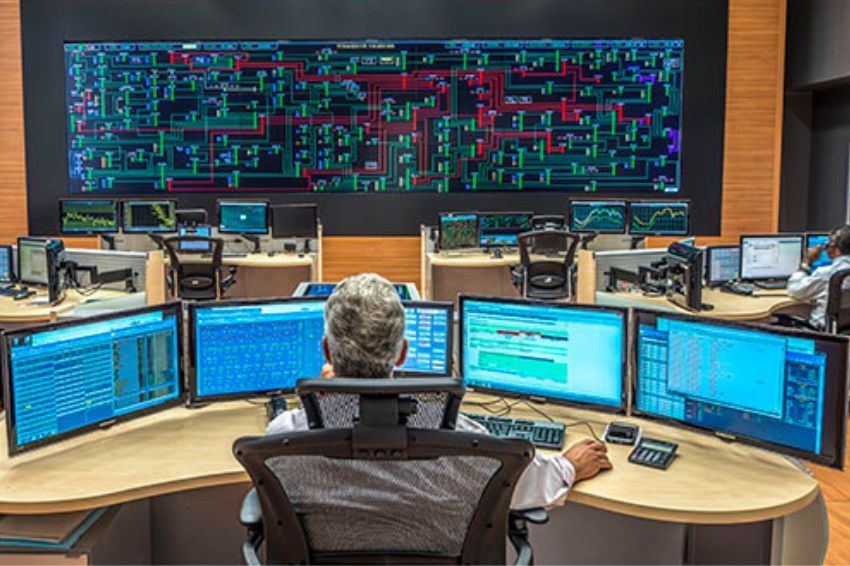
On July 1st, the Normative Resolution No. 964, of December 14, 2021, ANEEL (National Electric Energy Agency), which provides for cybersecurity rules to be adopted by agents in the electric energy sector.
The resolution is extremely important, as it defines the guidelines to be adopted by regulated agents in the energy sector with a view to cybersecurity risk mitigation.
Its application applies to concessionaires, permit holders, authorized electric energy services or installations and entities responsible for operating the system, selling electric energy or managing resources arising from sectoral charges, with the aim of mitigating risks related to incidents. cybersecurity in the electricity sector.
In this context, the main risks related to cybersecurity include possible interruption in the energy supply, the impossibility of carrying out technical operations by regulated agents and possible loss of data.
In relation to risks related to the continuity of operations, it is worth remembering cyber attacks such as “ransomware" [1] suffered last year by Colonial pipeline, one of the largest oil pipeline networks in the United States.
This action resulted in the company's operations being halted, causing the US government to declare a state of emergency in 17 states, due to the interruption of fuel flow.[2]
Resolution 964 presents guidelines for the actions of regulated agents in cybersecurity. Such guidelines include, among others, the need to adopt norms, standards and references of good practices in cyber security and the actions of agents to identify, diagnose and respond to cyber incidents, as well as disseminate a cyber security culture.
To this end, the resolution highlights the need for regulated agents to have a Cybersecurity Policy, which must adhere to the guidelines established in the regulation, compatible with the sensitivity of the data and information under the responsibility of the agent and with the relevance of the installation in the context of the SIN (National Interconnected System).
For the Cybersecurity Policy to be aligned with the provisions of the resolution, it must provide, among other aspects: criteria for classifying the data and information used by the agent, according to their relevance; procedures and controls to reduce vulnerability to incidents; and the adoption of technical measures to ensure the security and traceability of critical information.
Additionally, the resolution establishes specific obligations for regulated agents, such as, for example, that a person responsible for the Cybersecurity Policy is designated, as well as that this regulation is approved by the agent's Board of Directors (which may be unique for the entire economic group ) and reviewed periodically.
Another important aspect highlighted by the resolution is the duty of the regulated agent to internally disseminate, among its employees, the culture of cybersecurity, mainly through the implementation of training programs and the adoption of measures to raise awareness and education on aspects of cybersecurity .
Regarding cyber incidents, the resolution requires the Cyber Security Policy to define the parameters to be used in assessing the relevance of cyber incidents, as well as establish procedures for preventing, treating and responding to such incidents, which can be done, for example, through the development of an incident response plan.
Furthermore, agents are required to notify the designated sector coordination team in the event of major cyber incidents (as defined in the Resolution), which substantially affect the security of the facilities, operation or services to users or of data.
As can be seen, the resolution presents a basic framework to be implemented by regulated agents in the electricity sector, with the objective of minimizing the systemic risk arising from a possible cyber incident, developed in connection with the National Strategy for Security in Critical Infrastructures, established for the Decree No. 10.569/2020.
[1] “Ransomware” attacks can be defined as a type of “data hijacking” in which the criminal agent manages to invade systems and make them unavailable, demanding the payment of a “ransom”, usually in bitcoins, to restore servers and not disclose information accessed improperly.
[2] UNITED STATES SENATE. “America's data held hosting: case studies in ransomware attacks on American companies”. Staff Report – Committee on Homeland Security and Governmental Affairs. March 2022. Accessed June 30, 2022
* Paulo Lilla and Carla Segala are, respectively, partner and lawyer in the Technology, Data Protection and Intellectual Property area of the Lefosse office

Comments
Comments are moderated before publication.Comments should be respectful and contribute to a healthy debate. Offensive comments may be removed. The opinions expressed here are those of the authors and do not necessarily reflect the views of the author. Canal Solar.